 Phone : +974 44420050

 Doha, Qatar



Every organization with any scale now has some population of applications built outside formal IT development: low-code workflow tools, spreadsheet-based systems with embedded logic, and departmental automation built by whoever had the time and access to build it.
The debate worth having is not whether this exists. It clearly does.
The debate is what IT's posture toward it should actually be.
One position is that central IT should restrict low-code and citizen development tooling, require all new applications to go through a formal intake and build process, and treat anything built outside that process as a finding to remediate. The argument is straightforward: applications built without appropriate security and governance review can create data exposure, access-control and maintenance risks.
The opposing position is that restricting the tools may not eliminate the underlying activity. Business users still have operational problems to solve, and if the sanctioned platform disappears, they may move to spreadsheets, personal tools or other systems that provide even less visibility and control.
There is also a third possibility: bring citizen-built applications into a formal governance framework without treating every application as if it carries the same level of risk.
That could mean classifying applications according to the data and systems they access, applying stronger review to business-critical applications, assigning an owner to every production application, and ensuring identity, access and audit controls are built into the platform.
But that raises another question.
If a citizen-built application has been running for two years without an incident, does that provide meaningful evidence that it is low risk, or does it simply mean nobody has reviewed it closely?
And who should ultimately decide how much risk the organization is willing to accept: IT, the business unit that built the application, or a shared governance function?
Where does your organization stand today: should citizen-built applications be restricted, formally governed, or actively encouraged within defined guardrails?



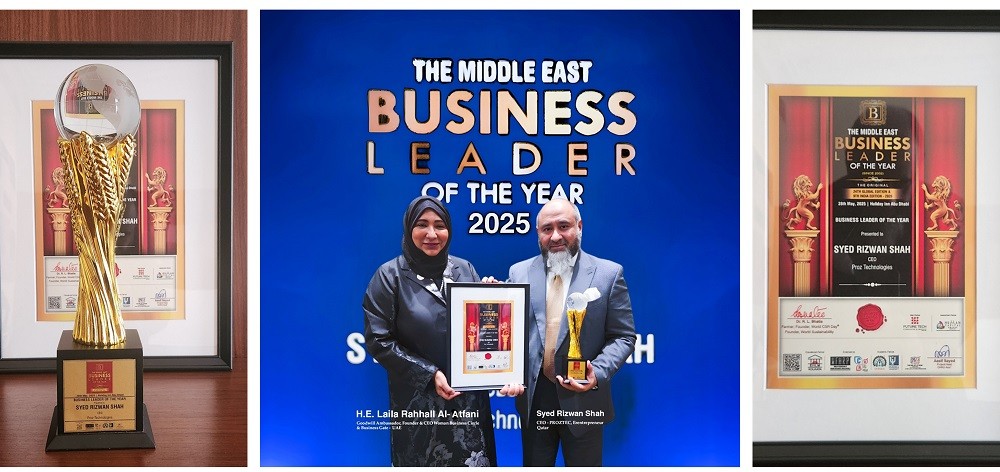 Celebrating Excellence: Mr. Syed Rizwan ...