 Phone : +974 44420050

 Doha, Qatar




Most cloud conversations still open
with the same three questions: what will it cost, how will it scale, how
available will it be. Those questions haven't gone away. But for organizations
running sensitive, regulated or mission-critical workloads, a fourth question
has moved up the agenda: who actually controls this environment, and under what
conditions can that control be exercised?
That question is what cloud
sovereignty is about, and it's increasingly a design input rather than a
compliance afterthought.
Cloud sovereignty concerns the degree
of control an organization retains over its data, infrastructure and
operations, in line with its legal, regulatory and strategic obligations. It
overlaps with data residency but isn't the same thing. Residency asks where
data physically sits. Sovereignty asks a wider set of questions: which
jurisdiction's laws apply, who can compel access, and how dependent the
organization is on a provider or geography it doesn't fully control.
The right answer differs by workload
and by regulatory environment, which is exactly why it needs to be assessed
deliberately rather than assumed by default.
A recent development in Qatar shows
these questions playing out in practice. In February 2026, Qatar's Ministry of
Communications and Information Technology announced an agreement with Oracle to
establish an additional dedicated government cloud region, part of a broader
initiative running through 2025–2028. The goal, according to the Ministry, is
to increase capacity, improve operational redundancy and strengthen the
geographic resilience of the cloud infrastructure supporting government
entities.
It's worth being precise about what
this does and doesn't tell us. It confirms that capacity, redundancy and
geographic resilience are active priorities for government cloud infrastructure
in Qatar. It does not, on its own, establish that Qatari enterprises broadly
are adopting a sovereignty-first cloud model, that's a separate question each
organization still has to answer for itself, based on its own workloads and
obligations.
A common assumption is that taking
sovereignty seriously means pulling everything back on-premise. In practice,
few organizations need, or can afford, to run every workload that way. A more
useful approach treats sovereignty as one variable in a broader placement
decision, applied differently across:
•
Highly
sensitive or regulated workloads
•
General
business applications
•
Data-intensive
analytics and processing
•
Development
and test environments
•
Disaster-recovery
environments
•
Public-facing
applications
Each category carries a different mix
of security, performance, cost and control requirements. The architecture
question isn't “cloud or not”, it's which environment fits which workload.
Data location and flow. Map where primary data, replicas and
backups actually live, including the secondary services and integrations that
can quietly create dependencies elsewhere.
Workload sensitivity. Not every system carries the same
regulatory or business weight. Classify workloads by criticality and data
sensitivity before deciding where they belong.
Resilience and recovery. Moving to the cloud doesn't remove
the need for failover and recovery planning , it changes what that planning
looks like.
Access and governance. Physical location is only one lever.
Identity management and privileged access shape how well an environment is
actually protected, regardless of where it sits.
Flexibility over time. Requirements shift. An architecture
that can absorb new regulatory or business demands without a full rebuild is
worth more than one optimized only for today's constraints.
It's easy to conflate the two, but
they answer different questions. Sovereignty is about control and jurisdiction.
Resilience is about withstanding and recovering from disruption. Qatar's
National Cyber Security Strategy names cyber resilience, response and recovery,
and continuity of critical services among its strategic objectives, a useful
reminder that resilience planning has its own dedicated focus, separate from
where control formally sits.
1.
Classify
critical workloads and data by sensitivity and business impact.
2.
Map
data locations, replicas and dependencies.
3.
Identify
the regulatory and contractual requirements that actually apply.
4.
Review
identity and privileged-access controls independent of location.
5.
Assess
disaster-recovery and failover requirements.
6.
Evaluate
placement options against the above, workload by workload.
7.
Revisit
the architecture on a regular cycle as requirements evolve.
These evaluations typically draw on
CIOs, CTOs, security and compliance leaders, and the business owners of the
workloads in question. Cloud sovereignty is rarely a decision one function can
make alone, since it touches legal obligation, technical architecture and
day-to-day operations at the same time.
Cloud sovereignty is best treated as
a design constraint, not a destination. Enterprises that get it right aren't
the ones that centralize everything in one environment for the sake of control, they're the ones that can explain, workload by workload, why each one lives
where it does. That clarity is what regulators, boards and customers are
increasingly going to expect.


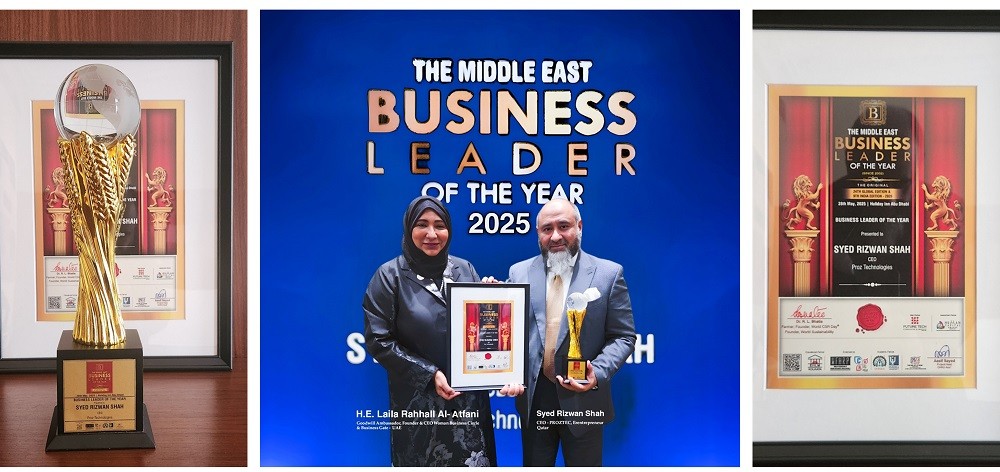 Celebrating Excellence: Mr. Syed Rizwan ...